Beyond ChatGPT: Give Your Assistant Reach Into Your Systems
ChatGPT, Claude, Copilot and Gemini all draft well and none of them can see your CRM. What changes when the assistant people already use can reach the systems they work in, and what IT needs before it allows that.
TL;DR
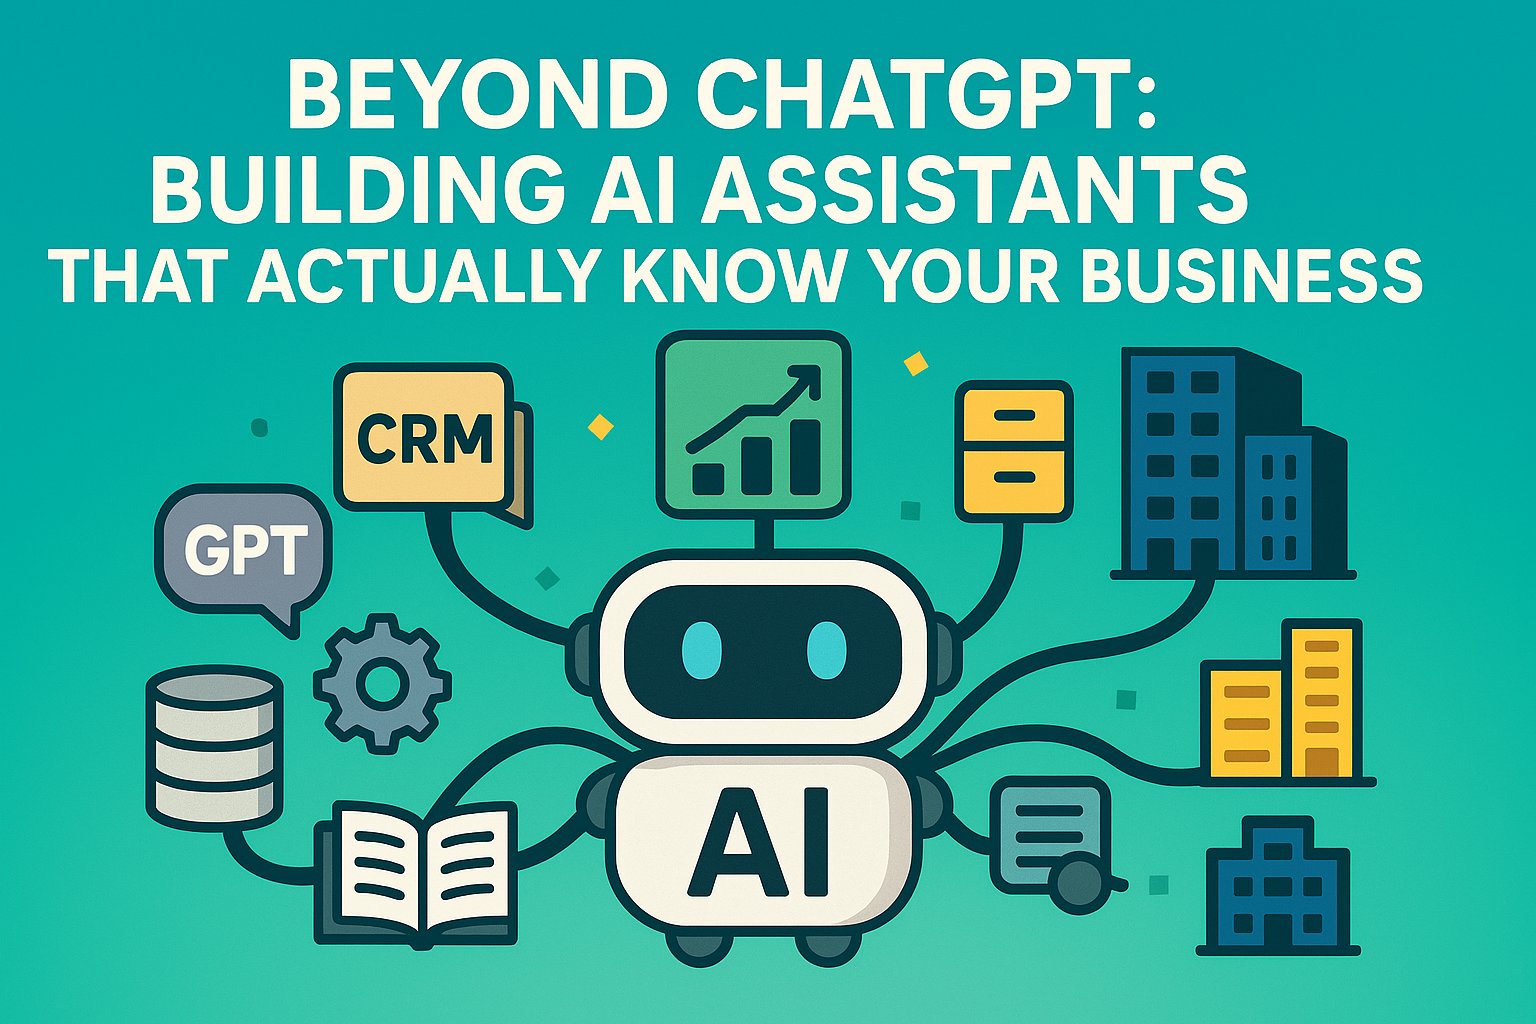
The title of this post used to mean "ChatGPT is generic, you need a business-aware AI instead". That is not the argument any more. ChatGPT, Claude, Copilot and Gemini are all good enough, and all of them can reach your systems over MCP. "Beyond ChatGPT" now means beyond the chat box: the assistant people already use, able to look things up and act in the systems they work in, with IT able to say who may do what.
What an assistant does today
Ask a chat assistant to draft a reply to an upset customer and it will produce a good draft. Ask it whether that customer's order has shipped and it cannot tell you, because it cannot see your order system. So the person copies the order number, opens fulfilment, reads the status, pastes it back, asks for a redraft, and then opens the ticketing tool to log the outcome. The assistant wrote some text. The work stayed manual.
That is the actual state of most enterprise AI rollouts: broad access to a very capable writer that has no reach. It is also why so many of them report adoption and no measurable effect.
What changes with reach
Give the same assistant the ability to look up the order, read the customer's history and open the ticket, and the request becomes "sort this out". The assistant checks fulfilment, sees the delay, drafts the reply with the real delivery date, proposes a goodwill credit and logs the case. The person reads the proposal and approves the credit. One exchange instead of five tool switches.
The mechanism is the Model Context Protocol. A system is exposed once as an MCP server; every assistant that speaks the protocol can then discover and call its tools. ChatGPT, Claude, Copilot, Gemini and the coding agents all do. You do not have to choose a "business-aware" assistant. You give the one you have somewhere to reach.
A few examples of what that looks like in ordinary jobs:
- Sales. "Prepare me for the 2pm call": the assistant pulls the account from the CRM, the open tickets from support, last quarter's invoices from billing, and writes the brief.
- Finance. "Which suppliers are over their PO this month": the assistant queries the ERP and produces the list with the variance, instead of someone exporting to a spreadsheet.
- IT support. "Reset access for the new starter in Marketing": the assistant checks the identity provider group, proposes the change, and a person approves before it runs.
- HR. "What is our parental leave policy in the Netherlands": the assistant reads the current policy document rather than a version it saw in training.
None of these are exotic. They are the ordinary work of the ordinary day, done from the tool the person already has open.
Why IT says no
Here is the part the 2025 version of this post skipped. The moment an assistant can reach the CRM, the ERP and the identity provider, it has to be governed like a person reaching them. And the protocol that gives the assistant reach does not decide which person may use which tool. It authenticates a client to a server; an authorised client then sees everything the server exposes to it. "Read a customer record" and "read every customer record" are the same tool. Proposing a credit and issuing one are both just calls.
So the security review asks five questions, and a pilot built directly on an assistant and a few servers cannot answer them:
- Who is allowed to use this tool?
- What exactly may they do with it, on which records?
- What happens when the assistant tries something risky?
- Where does the data go?
- Can you prove all of that afterwards?
This is why "beyond ChatGPT" projects stall. Not because the assistant is generic, but because reach without governance is unapprovable.
What makes it approvable
Each person gets one governed connector, assigned through the groups they already hold in the identity provider. It carries every tool and every Skill they are entitled to into whichever assistant they use. Someone in Finance sees Finance tools; a new starter in Sales has Sales tools on day one and loses them the day they leave. Policies are evaluated on the actual arguments of a call, so a read on one record and a bulk export are different decisions. Calls that need a human are held for approval. Every call is logged with who, what, when and why, and cost is attributed to the team that incurred it.
That is what Palma does. The assistant does not change and the systems do not change. What changes is that the five questions have answers, and the pilot goes to production.
Where to start
Pick one team and the two or three systems they actually use. Most of those already have an MCP server. Connect the identity provider, set reads open and writes behind approval, and give the team the assistant they already have with those tools in it. Take the audit trail to the security team at the end of the first week. Then let the second team inherit the same servers.
If you want to work out which team to start with, book thirty minutes and bring the list of assistants already in use; there are usually more than IT thinks.
Read More
The Hidden Cost of Disconnected AI in the Enterprise
An assistant that cannot reach your systems saves a few minutes of drafting and leaves the work where it was. Where the cost actually sits, and what it takes for IT to let the assistant reach further.
One Connector, Every AI Client: Per-Client Integration Fails
The moment you run a second assistant or a second system, per-client integration turns into N times M work and N audit surfaces. Serving capability over MCP collapses it back to one governed layer.
Book a demo
See what governed AI agents look like.
A 20-minute demo on your stack. We'll show Palma working with the agents, tools and identity provider you already run.
- Enterprise security
- Role-based access
- Instant integration